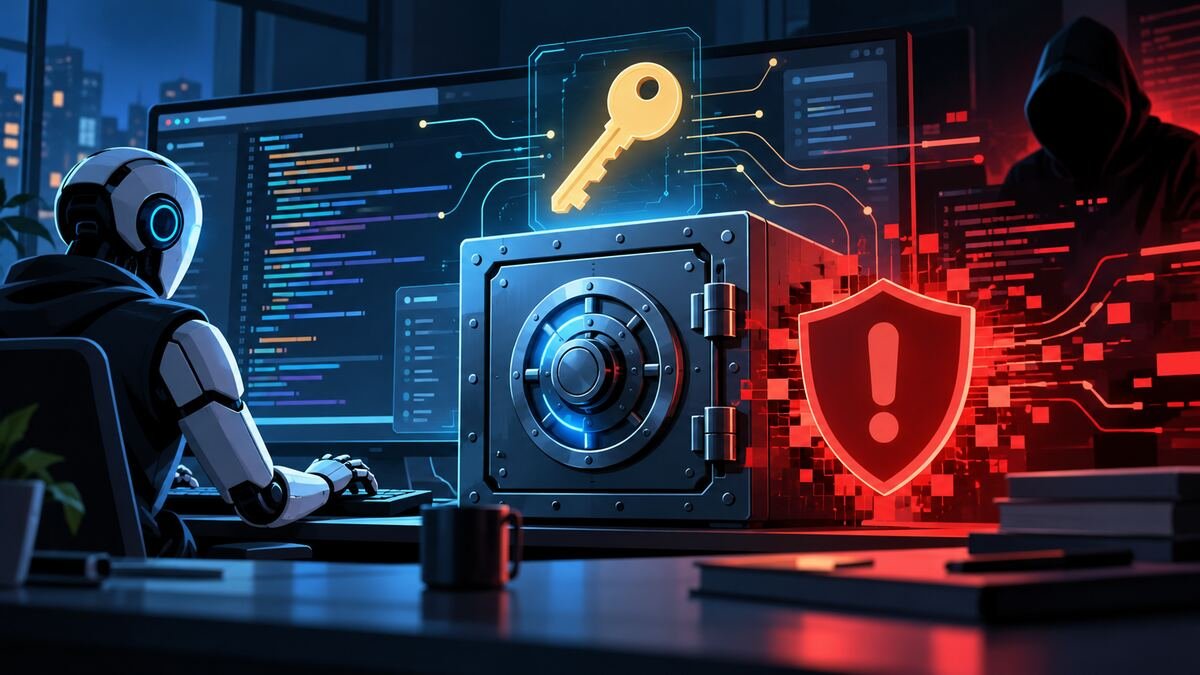
OpenCode has disclosed a security incident affecting 1.4% of its Console users. The company described it as related to a “large-scale distillation attack” and said the affected group was a subset of users who had external AI providers linked. The disclosure is developing, and the company has not publicly explained exactly what information was accessed or how the intrusion occurred.
What is confirmed so far
According to OpenCode’s October 17 statement, the incident happened the previous night and affected 1.4% of OpenCode Console users. OpenCode said it emailed affected users and that people who did not receive an email were not impacted. The term “distillation attack” was used by the company, but the public notice did not detail the attacker, target model, access method, or data involved.
That uncertainty is important. Some secondary reports have discussed the possibility that API keys saved for external providers could be at risk, but OpenCode’s initial public disclosure did not confirm what specific secrets or records were accessed. Users should follow direct notices from OpenCode and the affected provider rather than treating every unverified account as established fact.
Why connected API keys matter
A provider API key is a credential that allows a software tool to send requests to a model service under a particular account. If an application stores such a key to connect to an external provider, the key needs protections similar to other secrets: limited access, careful storage, rotation when exposure is suspected and usage monitoring. A compromised key can create unexpected charges or allow requests to be made under the account, depending on the provider’s controls.
That does not mean a key was necessarily taken in this incident. It explains why linked-provider users should pay attention to any direct notification and take a cautious approach if they stored credentials in the affected Console service.
Steps for OpenCode Console users
- Check the email address tied to OpenCode Console and read any incident notice carefully.
- If you were notified—or if you are unsure whether a connected key may have been stored in the affected environment—rotate that provider key from the provider’s own account dashboard.
- Review recent API usage, logs and billing for activity you do not recognize.
- Use separate, least-privilege credentials for development tools and set spending limits or alerts where available.
- Do not click links in unexpected incident emails; navigate to the provider’s official site directly.
- Keep secrets out of source files and use a secrets manager or environment-specific credential store.
If you use only the local OpenCode CLI and did not connect external providers through Console, do not assume that the incident necessarily applies to you; check the company’s latest notice for scope. Organizations should record which users and services had linked provider accounts and make credential rotation easy when an incident occurs.
A broader lesson for AI development tools
AI coding tools sit between developers and model providers. They can hold source code, project context, usage metadata and credentials that connect other services. Security reviews should therefore examine the entire chain: the editor or hosted console, provider API, repository permissions, logs and billing controls.
Teams can reduce exposure by limiting token scopes, using short-lived credentials where supported, separating test and production keys, and monitoring unusual usage. These practices are especially useful as AI agents gain the ability to run code or interact with live systems. Read our guide to AI agent access boundaries and our coverage of websites restricting autonomous agents.
Source: CyberStack’s incident summary, verified October 18, 2026, which links to OpenCode’s official statement. The precise data accessed remains undisclosed in the cited public notice.
Reader Discussions
No comments posted yet. Be the first to start the discussion!
Leave a Reply